The most vulnerable point in a modern estate is rarely the front door. It is the smart bulb in the guest suite, the pool controller humming beside the equipment pad, or the streaming stick nobody has touched since the day it was unboxed. When people ask me about the iot security risks home owners actually face, they usually expect a story about a hacker cracking a firewall. The reality is quieter, and far more common. An inexpensive, unpatched gadget quietly invites a stranger onto your network, and from that foothold, into everything else you own.
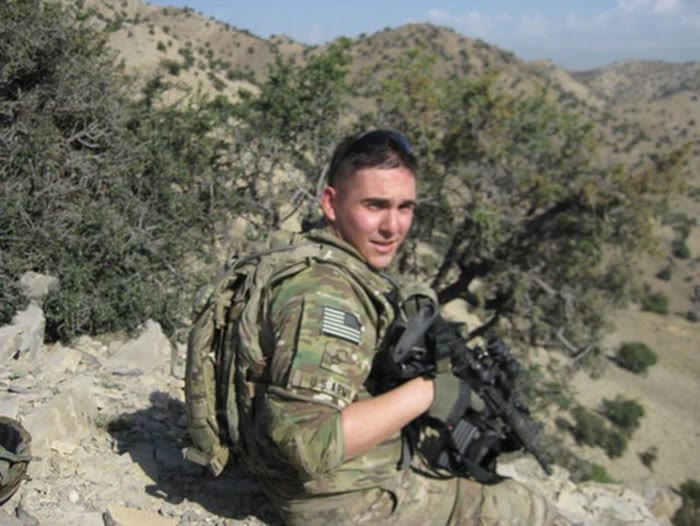
I spent years in the Army as an Electronic Warfare Officer, including a 2011 deployment to Afghanistan on a Counter-IED team. My job was to read the electromagnetic environment: every emitter, every signal, every device that did not belong. A luxury smart home is the same problem in nicer packaging. Every connected thing is an emitter and an attack surface. The question is never whether devices are talking on your network. It is whether you know what they are, what they are saying, and who else is listening.
Every Connected Device Is an Emitter
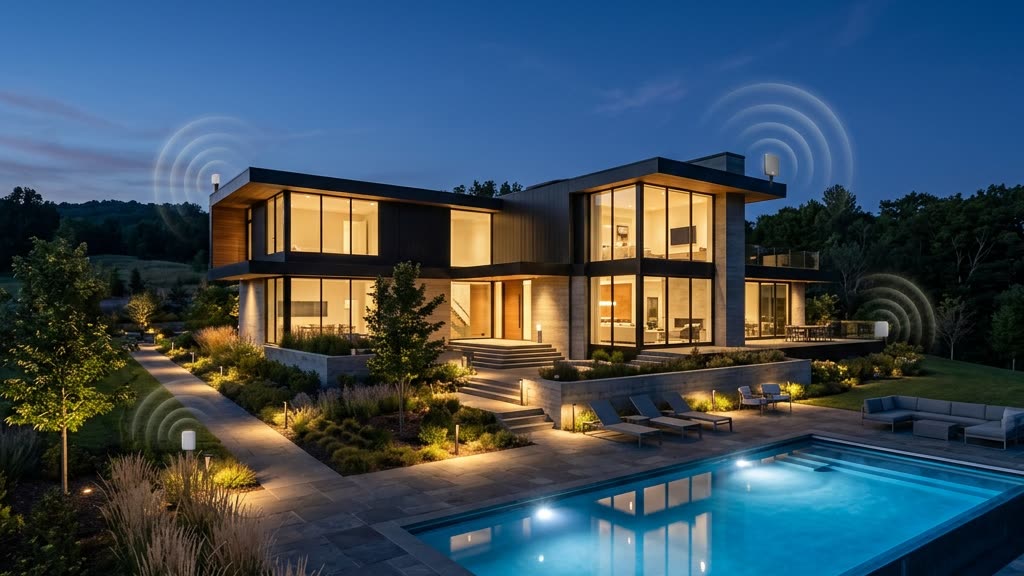
In electronic warfare, we treated the spectrum as terrain. You cannot defend ground you have not mapped. The same discipline applies to a residence full of connected technology. A high-end home today can carry dozens of internet-enabled devices: lighting, thermostats, irrigation, pool and spa controllers, cameras, smart locks, garage systems, televisions, voice assistants, refrigerators, even climate-controlled wine rooms and motorized art.
Each of those devices runs software. And most of it was built to a price and a shipping deadline, not to a security standard. The company that makes a fifteen dollar smart plug and the company that protects your bank’s infrastructure are not playing the same game. Cheap IoT hardware often ships with default passwords, rarely receives security patches, and frequently phones home to servers you will never audit. Attackers understand this better than most homeowners do. They do not waste effort defeating your strongest defense. They scan for the weakest emitter on the network and treat it as an unlocked side door.
The federal government has been sounding this alarm for years. The Cybersecurity and Infrastructure Security Agency publishes ongoing guidance on connected-device risk, and you can start with the plain-language material at CISA (opens in a new tab). The National Institute of Standards and Technology has built an entire body of work on baseline security for IoT devices, available through NIST (opens in a new tab). Both agencies keep arriving at the same conclusion: the devices are not going away, so the discipline has to come from how you deploy and manage them.
Step One: Inventory What You Cannot See
You cannot protect what you have not counted. This is the first move, and most estates skip it entirely.
I have walked properties where the owner confidently listed eight or ten smart devices, and a proper network scan revealed three or four times that number. The forgotten ones are almost always the culprits. A contractor’s camera left connected after a renovation. A smart TV in a rarely used media room. A pool automation gateway installed by a subcontractor who set the password to something generic and never told anyone. A voice assistant a houseguest paired and left behind.
Build a Living Device List
A real inventory is not a mental note. It is a written, maintained list that records, for every connected device: what it is, who installed it, what network it sits on, what account controls it, and whether it still receives updates. When a household changes staff, sells a vehicle with a paired app, or finishes a construction project, that list gets reviewed. In signals work we called this a common operating picture. In a home, it is simply knowing your own terrain before someone else maps it for you.
If you have never done this, our home network security guide for high-net-worth families walks through the process in more depth. The exercise is not glamorous. It is the single highest-value hour you will spend on your digital security.
Step Two: Isolation, Not Just a Wall
Here is the principle that changes everything: a device should only reach what it genuinely needs to reach.
Your pool controller has no legitimate reason to sit on the same network as the laptop where you handle wire transfers, your family’s phones, or the storage drive holding tax records and estate documents. Yet in the default configuration most installers leave behind, every device shares one flat network. Compromise the weakest thing on that network, and an intruder has a clear line of sight to the most sensitive.
Segment the Network
The fix is segmentation. At minimum, connected gadgets belong on a separate network from the devices that hold your financial and personal life. Many capable routers support a guest network or, better, virtual LANs that keep IoT traffic walled off from your primary systems. Think of it as a moat between the outbuildings and the main house. If the smart bulb is breached, the damage stops at the bulb.
Getting this right starts at the router, which is the true perimeter of your digital estate. If yours has never been properly configured, our router hardening checklist is the place to begin. Changing default credentials, disabling remote administration you do not use, and enabling automatic security updates on the router itself will close a surprising number of doors before you touch a single smart device.
Step Three: Firmware Discipline
Firmware updates are boring. They are also, quietly, the most important habit on this list.
Every patch a manufacturer releases is a public record of a weakness. Once that update ships, the underlying flaw is documented, and anyone paying attention knows exactly what to exploit on devices that have not applied it. An unpatched device is not a neutral risk that stays constant. It becomes more dangerous over time as the vulnerability becomes common knowledge.
Practical discipline looks like this. Enable automatic updates wherever the device offers them. For devices that require manual updates, put a recurring reminder on the calendar and actually keep it. And when a manufacturer stops issuing security updates for a product, treat that device as end-of-life and retire it, even if it still works. A camera that no longer receives patches is a liability dressed up as a convenience. The Federal Trade Commission has written extensively for consumers on device support and update expectations, and the guidance at the FTC (opens in a new tab) is worth reading before your next smart-home purchase.
There is a purchasing lesson buried here too. When you or your designer selects new connected products, favor manufacturers that publish a clear security update commitment. The cheapest device on the shelf is almost never the cheapest device to own once you account for the risk it carries.
When Monitoring Beats Hoping
Inventory, isolation, and firmware discipline dramatically shrink your exposure. They do not eliminate it, because no home is static. Guests arrive with their own hardware. Staff connect new tools. Vendors install equipment. The network you hardened in January is not the network you are living on in July.
This is where continuous monitoring earns its place. As the exclusive reseller partner for GuardDog AI, our veteran-owned team deploys, integrates, and tunes their enterprise-grade intrusion-detection platform inside private residences. It is not our technology, and I will never pretend it is. It is a proven enterprise system that we adapt to the realities of a high-value home, so that when an unfamiliar device appears or a known device starts behaving strangely, someone notices in real time rather than in the aftermath. You can read more about how that fits into a complete protection strategy on our GuardDog overview.
The threats rarely arrive as a dramatic breach. More often they begin with a convincing message aimed at a family member or an assistant, which is why device security and human awareness belong in the same conversation. If that side of the risk interests you, our field note on phishing scams targeting wealthy families covers the tactics we see most. For families across Southwest Florida, our Fort Myers team handles these assessments discreetly and in person.
Frequently Asked Questions
What is the most dangerous IoT device in a luxury home?
There is no single answer, and that is the point. The most dangerous device is whichever one you have forgotten about: unpatched, on your main network, controlled by an account nobody manages. In my experience it is often a camera or an automation gateway installed by a third party and never revisited.
Do I need to replace all my smart devices to be safe?
No. Most estates do not have a hardware problem, they have a management problem. Inventory, network segmentation, and consistent firmware updates address the majority of the risk with the equipment you already own. Replacement matters mainly when a device has reached end-of-life and no longer receives security updates.
Can’t my alarm company handle this?
Traditional alarm and camera providers secure doors, windows, and video. Very few monitor the data network those systems now depend on, and fewer still watch the dozens of other connected devices in a modern home. Physical security and network security are related disciplines, but they are not the same job.
How often should I update device firmware?
Enable automatic updates wherever possible so the answer becomes as soon as a patch is released. For devices that require manual updates, a monthly review is a reasonable rhythm. The key habit is retiring any device the manufacturer no longer supports.
Securing a connected estate is not about fear, it is about knowing your own terrain before anyone else does. If you would like a discreet, professional assessment of the devices on your network and how they are isolated, I invite you to request a private consultation or call our team directly at (239) 710-1772. We will map what you have, close the doors that matter, and give you a plan you can actually maintain.